Payment network risk, bots and endpoint defense
Investigate masking and automation with trusted inputs, relevant account context and controls at the protected endpoint.
Summarize with AI
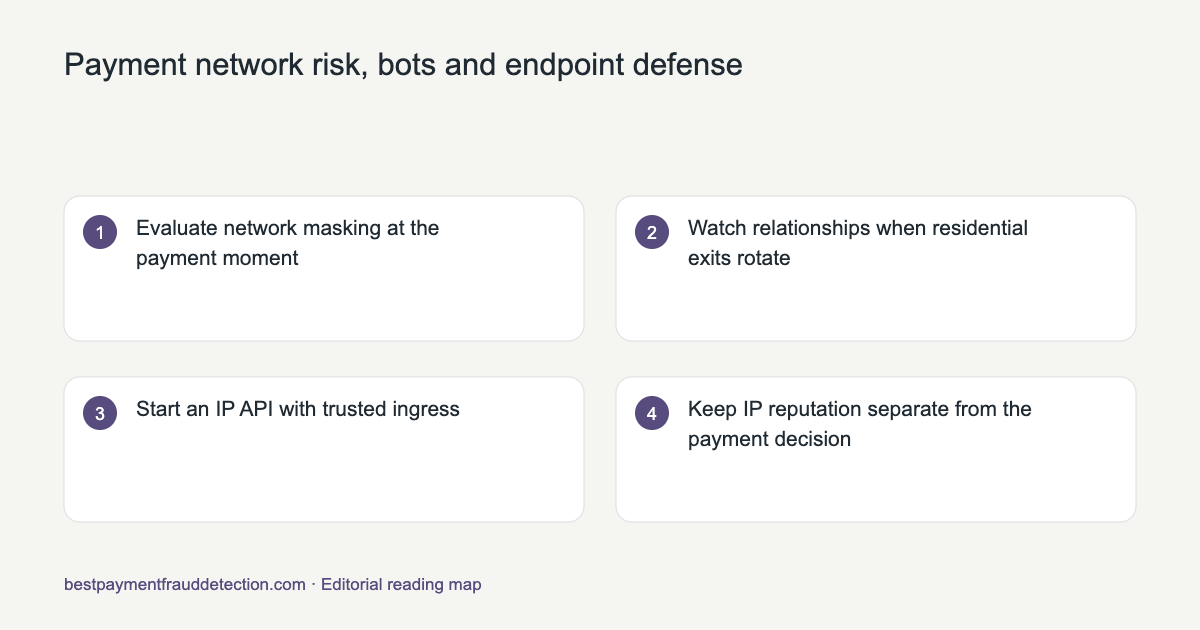
Evaluate network masking at the payment moment
IPQualityScore and MaxMind provide IP intelligence; ShieldLabs, Castle and Maskbreak combine relevant network checks with broader visit evidence. Compare VPN, Tor, datacenter, residential and mobile coverage separately. An anonymizer label describes the route, not intent. Retain the field reason and freshness, then combine them with order and account behavior. Corporate egress and privacy services need legitimate controls in your evaluation.
Reference: IPQualityScore: product families.
Watch relationships when residential exits rotate
Residential or mobile proxy traffic can appear on consumer networks, so network ownership alone is insufficient. MaxMind documents confidence, provider and last-seen signals in specific products. Connect those signals to device continuity and payment velocity across changing addresses. Apple Private Relay and carrier NAT are useful legitimate comparison groups. Measure detection errors separately from policy errors where a correctly labeled proxy shopper was unnecessarily declined.
Reference: MaxMind: anonymizer and proxy data.
Start an IP API with trusted ingress
Obtain the client address from your trusted proxy chain and prevent callers from supplying arbitrary forwarding headers. Check IPv4 and IPv6 entitlement, Tor and hosting fields, freshness and error responses. Apple publishes Private Relay address and location feeds; keep that service distinct from generic malicious proxies. An IP-only lookup does not return browser evidence. Account for caching and repeated order attempts in the billable workload.
Reference: Cloudflare: HTTP headers.
Keep IP reputation separate from the payment decision
An IP fraud score summarizes a provider's network evidence using its own scale. Device reputation concerns the observed environment and related activity. Preserve both, plus reasons and observation time, rather than adding incompatible vendor scores. For IPQS or another provider, verify the actual response fields and plan. A good score cannot authorize a card, and a shared bad address should not erase a trusted shopper's history.
Reference: MaxMind: proxy and anonymizer data.
Investigate location mismatches with uncertainty
Location spoofing can create disagreement among IP geolocation, device context and permitted location inputs. Browser geolocation accuracy is an uncertainty measure, not a guarantee that an address is exact. A VPN can locate the exit instead of the shopper. Review timestamps, session continuity and the protected payment action. Travelers and mobile-network changes belong in your legitimate cohort before you enforce a geographic rule.
Reference: MDN: geolocation accuracy.
Read an anonymity checker as a diagnostic
An anonymity check can reveal the current exit IP, routing labels and browser properties visible to that checker. It cannot certify that every website sees the same signals or that a session is untraceable. Use results to diagnose privacy settings or a known network transition. For payment evaluation, compare checker output with the actual protected session rather than interpreting one clean screen as proof of a legitimate order.
Reference: W3C: mitigating browser fingerprinting in web specifications.
Contain automation before it reaches payment authorization
Bot detection belongs at exposed signup, login and checkout endpoints. Cloudflare provides request-level bot scoring; HUMAN spans advertising, application and account protection; Arkose Labs combines fraud prevention with agent controls. Choose by the protected route and required response. A payment team should measure legitimate checkout completion and fraudulent authorization attempts together. A low bot score alone does not establish that the cardholder is fraudulent.
Reference: Cloudflare: bot scores.
Join the browser check to the payment attempt
Send collection references to your server with the order attempt, then retrieve trusted results before the protected action. Keep secret credentials server-side. WordPress plugins and hosted widgets still need endpoint protection. For Turnstile, server-side Siteverify validation is mandatory; tokens last five minutes and are single-use. Define timeout and duplicate-submission behavior before a customer presses Pay twice.
Reference: Cloudflare Turnstile: validate the token.
Give AI shopping agents an explicit checkout policy
An AI agent can browse legitimately and still lack permission to place an order. Separate identification of automation from authorization to spend money. Verify declared crawlers through documented provider methods rather than trusting a user-agent string. For shopping agents, define permitted catalog access, account consent, spending authority and transaction confirmation. Track these populations separately from credential attacks and card-testing scripts.
Reference: Google: verify crawler and fetcher requests.
Replace repeated puzzles with appropriate checks
CAPTCHA alternatives include Turnstile, device or session risk checks, rate limits, passkeys and supported Private Access Tokens. Apple describes tokens that attest legitimate devices and users while protecting identity. They do not establish payment entitlement or available funds. At checkout, validate challenge results on the server and reserve additional authentication for a justified payment risk. Compare completion rates for accessibility and privacy-browser cohorts.
Reference: Apple: Private Access Tokens.
Protect stored cards from credential stuffing
Credential stuffing reuses breached username-password pairs; password spraying tries one common password across many accounts. OWASP recommends MFA and layered defenses. Limit attempts across accounts and related devices as well as IPs, inspect successful logins following repeated failures, and step up before saved-card use or address changes. A valid password should not erase the risk accumulated earlier in the access sequence.
Reference: OWASP: credential stuffing prevention.
Worked network example: a privacy relay and a card probe
Hypothetical example: two sessions share a relay category. One belongs to a returning account placing its ordinary order; the other attempts many low-value payments with repeated failures. Keep the network observation in both cases, but investigate their different action histories. A policy built only on the relay label loses that distinction.
| Layer | Example evidence | Decision use | | Network | Exit category and freshness | Routing context | | Automation | Repeated scripted submissions | Endpoint containment | | Account/order | Prior history and authorization | Proportionate payment response |
Continue with Account access and linked identities before payment for the next evidence layer.
Sources
- IPQualityScore: product families · read
- Maskbreak: live-visit checks and IP lookup · read
- MaxMind: anonymizer and proxy data · read
- Apple: prepare for Private Relay · read
- Cloudflare: HTTP request headers · read
- OWASP: REST security · read
- OWASP: transaction authorization · read
- MDN: geolocation accuracy · read
- OWASP: authentication · read
- W3C: mitigating browser fingerprinting in web specifications · read
- MDN: OfflineAudioContext · read
- Cloudflare: bot scores · read
- OWASP: automated threats to web applications · read
- Cloudflare Turnstile: server-side validation · read
- HUMAN: application and advertising product families · read
- Arkose Labs: current platform scope · read
- Stripe: idempotent requests · read
- Google: verify crawler and fetcher requests · read
- OWASP: authorization guidance · read
- Apple: Private Access Tokens · read
- OWASP: credential stuffing prevention · read
- NIST: authentication and authenticator management · read
- OWASP: forgot password guidance · read
- Primary source: www.fraudfilter.io · read
- Primary source: www.fraudfilter.io · read
- Primary source: proxy6.net · read
- Primary source: oxylabs.io · read
- Primary source: brightdata.com · read
- Primary source: shieldlabs.ai · read
- Primary source: castle.io · read
- Primary source: www.hcaptcha.com · read
- Primary source: friendlycaptcha.com · read
- Primary source: altcha.org · read
- Primary source: prosopo.io · read
- Primary source: www.mtcaptcha.com · read
- Primary source: en.vaptcha.com · read
- Primary source: docs.cloud.google.com · read
- Primary source: help.sitechecker.pro · read
- Primary source: www.incognia.com · read
- Primary source: www.kasada.io · read
Continue reading
FAQ
Should every VPN payment be declined?
A VPN label describes routing. Review it alongside account, device, order and authentication evidence, with legitimate corporate and privacy-network customers in the evaluation.
How long is FraudFilter’s trial?
For gateway input, FraudFilter advertises a seven-day trial without a credit card. Its pricing page separately lists 199 US dollars per month and a fifteen-day refund policy. Keep trial duration and refund conditions distinct when comparing evaluation access.
What is the Proxy6 anonymity check?
For gateway input, Proxy6 offers a public anonymity-check page for selected IP and browser observations. It is a diagnostic route rather than a certification of invisibility to every site. Review displayed scope and access separately from a production API contract.
Which tools fit IP enrichment versus broader bot or account risk?
For payment networks, choose the routing evidence and endpoint response. IPQualityScore and MaxMind are relevant for IP intelligence. ShieldLabs or Castle add broader environment/account context. For request-level bot enforcement, compare Cloudflare, HUMAN and Arkose against the required routes and response integration.
Which seven CAPTCHA-related brands are relevant to compare?
A source-backed shortlist is Cloudflare Turnstile, hCaptcha, Friendly Captcha, ALTCHA, Prosopo, MTCaptcha and Arkose Labs. For payment networks, choose the routing evidence and endpoint response. Compare server validation, accessibility, supported surfaces and data handling. Broader vendors can include account or agent features beyond a challenge, so inspect the proposed product rather than assuming all plans are puzzle-only.
Can a residential VPN guarantee that a site will not recognize a visit?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. Choose a privacy service for the stated privacy requirement and its published data practices, rather than a promise of undetectability. A residential-looking exit does not remove account history, browser evidence or other observations available to a site. MaxMind explains how anonymizer intelligence concerns the exit. For a legitimate access problem, use the site’s supported authentication or support route. For your own system, evaluate privacy connections with known permission and expected results.
How should VAPTCHA be compared with reCAPTCHA?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. Compare the verification flow and backend integration rather than assuming “better” has one universal meaning. VAPTCHA’s FAQ distinguishes redirected SV verification from onsite EV verification and requires server confirmation. Google’s website assessment guide describes the reCAPTCHA backend assessment and token validity checks. Evaluate supported surfaces, accessible recovery, privacy/data handling, completion and replay behavior on your own authorized flow. The malformed comparison wording is interpreted here as a product-selection question, not a verified performance claim.
What is Sitecheckerbot?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. Sitechecker’s crawler documentation identifies SiteCheckerBotCrawler as its website-audit crawler and provides a current IP-list route. Audit crawling and fraud detection are different tasks. If you operate the site, manage intended crawl access through the documented robots/WAF configuration and verify the request source rather than trusting its user-agent alone. Seeing the name in a log does not establish that the visit is a harmful account bot.
Which options fit mobile-proxy and high-volume risk checks?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. For network enrichment, compare IPQualityScore and MaxMind. For additional device/account context, compare ShieldLabs, Castle and Incognia according to the required mobile/location surface. Specify expected peak requests, concurrency, IPv6 mix, freshness, latency distribution, rate limits and outage handling in a written offer. Use known legitimate proxy/relay users and confirmed abuse to choose proportional responses. A high-volume statement or proxy label cannot guarantee zero disruption to ordinary customers.
What should a mid-size ecommerce team evaluate when replacing Cloudflare bot controls?
For edge/application bot protection, compare Kasada, HUMAN and Arkose against the checkout, search, signup and login routes you use. Add ShieldLabs or Castle when account/device context is also missing. Inventory the current edge rules, trusted client-IP chain, challenge verification and permitted crawlers. Pilot the replacement on the same legitimate and abusive event populations, preserve a rollback path and confirm which provider owns each response. A migration should preserve required controls rather than replace a CDN name with an unrelated lookup API.